
Edward Awonaike
Sr. Industrial Cybersecurity Consultant @ Duke Energy Charlotte
About
• Application Security Assessments of Cloud and On Prem applications utilizing diverse Threat Modeling methodologies such as STRIDE, PASTA, Dread and OWASP Threat Modeling. • Provisioning and Deprovisioning of API implementations and integrations utilizing secure authentication, specific IP Whitelisting, API Gateways with secure third-party implementations such as Ping Identity, OKTA, DataPower. • Expert knowledge of diverse frameworks such as the SAMM, NIST 800-53, ISO 27002, COBIT control frameworks. • Thorough understanding of Agile software business requirements towards achieving project business goals and objectives, • Experience interpreting reports from commercial and open-source security tools for Static Application Security Testing and Dynamic Application security testing such as Fortify, Appscan, Check Marx, • Provide and publish weekly and monthly status reports of identified tactical and strategic risk finding to C-Level Officers such as the CISO and CIO. • Responsibility for driving enterprise level Risk tolerance strategy. • Provide walkthrough of the reports to all the stakeholders. • Implementation of Secure Architectural designs templates for Cloud Access Provisioning to support the CIA triad
United States
Charlotte Metro
Information Technology & Services
Project Management, Virtualization, VMware, Cisco Technologies, Active Directory, Disaster Recovery, Cloud Computing, Data Center, TCP/IP, System Administration, Enterprise Software, Information Security, Servers, Networking, Computer Security, Network Security, Security, Software Development, Management, Vendor Management
Experience
Sr. Industrial Cybersecurity Consultant
1898 & Co.

Kansas, United States
As a Sr. Cybersecurity consultant, I had the main responsibility for performing gap assessments utilizing diverse frameworks to identify key risk areas and prescribe mitigation plans and strategies for enhancing the cyber security program for our numerous clients Responsibility for generating additional revenue through the engagement of existing and potentially new clients for our numerous service offerings. Further responsibilities includes asset management, incident response, business continuity and disaster recovery for my assigned 1898 and co clients. Details of some of these assignments includes: • Redesigned and implemented numerous Cyber Security Program Industrial Control System for clients of the company. • Perform IT/OT Gap assessments utilizing approved IT frameworks such as NIST800-53/171, NERC CIP assessments for numerous 1898 and Co consulting clients. • Conduct network and application vulnerability assessments of OT environments for government and private enterprises utilizing tools such as Nessus, Tenable. Review and analysis of vulnerability scan results from various security tools. • Developed a library of IT Cybersecurity policies, standards and procedures for 1898 and Co as a service offering for the consulting services teams of 1898 and co. • Develop and deploy cyber and asset management programs with diverse tools such as Eyeinspect, Nozomi and Claroty packages. • Conduct application whitelisting. • Firewall Design, Management and Rules review. • Design network hardening. • Incident response and disaster recovery assessments and implementations. • Security Information and Event Management (SIEM) Package implementations. • Conduct reviews of Intrusion Detection System (IDS) Package implementation Develop Security Assessment Plans and Reports. • Review and implement NERC CIP compliance requirements. • Manage audit requirements for NERC CIP: Low, Medium and High Impact requirements, ISA/IEC 62443, NIST 800-53, 800-171, NIST CSF framework.
Executive Consultant
Cybersecurity and Privacy Corp
United States
Cybersecurity And Privacy Co Clients include Eversource Energy, Tenneco, Sentara Healthcare, ● Chair cybersecurity, infrastructure, and application security reviews of new and existing projects to include assessment of technical diagrams, solution designs, project charter, data flow diagrams, scope and design documentation which is then followed by the write up of Security Assessment Reports (SAR) for all assigned projects for the IT and OT security environments. ● O365 cloud migration to Azure and multiple business application migrations to Amazon Web Services. ● Perform gap analysis of all projects against established widely accepted information security best practices and information security policies. ● Provide consultation to business teams during the RFP engagement process of third-party vendors. ● Design and implementation of appropriate controls to mitigate identified risks in the OT and SCADA networks. ● Assessment of existing risk appetite for those projects that require some form of risk acceptance, exceptions and waivers and communication of these through the highest levels of executive leadership. ● Proficiency in ISDLS methodologies such as Waterfall and Agile. ● Proficiency in the application of the SABSA and TOGAAF frameworks. ● Review of high visibility and large implementation projects such as the Duke Energy CSOC, PII data encryption project sanctioned by the Duke board of directors. ● Proficiency with NERC CIP, FISMA HIGH, COBIT, PCI, ISO 17779/270013/3100/27002-13, NIST 800, IEC 62443, IEC 61850-3, SCADA, OT Environment and Frameworks. ● Developed centralized risk management processes and governance. ● Cloud assessments and migrations to include Microsoft Azure, Amazon web services. ● Application security recently reviewed developed within the last year include: ✓ Database monitoring tool SecureSphere. ✓ Data encryption tool HPE Voltage. ✓ VPN and MDM tool Netmotion. ✓ VPN MDM solution Airwatch
Sr. Cybersecurity Architect
PWC-IBM-INFY
Raleigh-Durham, North Carolina Area
• Implement and oversee Cybersecurity strategy enterprise assessments spanning across IBM business units. • Provide strategic direction to CISO and executive stakeholders.
Cybersecurity Architect
IBM
• Provide strategic risks direction to CISO and executive stakeholders. • Implement and oversee Cybersecurity strategy enterprise assessments spanning all IBM business units. • Develop, Apply and Integrate application security for internally developed and COTS applications within the IBM cloud, On-prem and Third-party vendor sites. • Liaise directly with BISO (Business Information Security Officers) of IBM business units to determine and escalate the resolution of identified risks deemed to be strategic to the enterprise for adequate mitigation and risk treatments • Responsibility for Merger and Acquisition IT Security Assessment activities. • Lead security strategic initiatives and assessments of IBM Cloud ‘Watson’. • Identification and Prescription of strategic security controls of other cloud offerings within Microsoft Azure and Office 365. • Cybersecurity and application security assessments of IBM applications hosted on Amazon Web Services, Microsoft Azure and IBM Watson Cloud. • Secure Identity Access Management provisioning for cloud-based implementations. OAuth, 2F authorization. • Secure API integrations. • Aggregate reports from multiple sources of security event and incident management tools (SIEM), log management, user-based behavioral analytical monitoring tools for review and threat and vulnerability mitigation
OT Cybersecurity Consultant
Entergy
• Perform the NERC CIP compliance assessments for the Entergy nuclear network segments to meet and exceed the eleven standards requirements against cybersecurity attacks. • Deep packet inspection of parameters to provide granular control over the ICS protocol payload by identifying and blocking or restricting access to risky industrial protocols. • Monitor for Real-time threat intelligence updates to battle emerging and advanced cyber threats. • Implementing AirGap (Data-Diode) network segmentation design for the Waterford power plants. • OT, ICS (SCADA and DCS) Network design and Assessment reviews. • Implementation and adherence to the Architectural Purdue Model. • Monitor personnel's adherence to CIP physical security policies and procedures via video surveillance. • Execute and utilize ISO 27002, NIST 800-53, IEC 62443, and IEC 61850-3 Standards and Frameworks • Provide mitigation for emergent, existing, and future security vulnerabilities in the IACS network and environment.
Sr Cybersecurity Architect
Duke Energy Corporation
● Chair cybersecurity architectural reviews for all incoming new and existing projects thru the ISDLC. ● SME for O365 Cloud Migration to Azure and multiple business migrations to AWS. ● Perform gap analysis of all projects against established widely accepted information security best practices and against existing Duke Energy Information security policies. ● Provide consultation to business teams during the RFP engagement process of third party vendors. ● Drive critical data assessments CDA’s for Nuclear Plant network segments. ● Design and Implementation of appropriate controls to mitigate identified risks. ● Assessment of existing risk appetite for those projects that require some form of risk acceptance, exceptions and waivers and communication of these through the highest levels of executive leadership. ● Proficiency in ISDLC methodologies such as Waterfall and Agile. ● Review of high visibility and large implementation projects such as the Duke Energy CSOC, PII data encryption project sanctioned by the Duke board of directors. ● Proficiency with NERC CIP, FISMA HIGH, COBIT, PCI, ISO 17779/270013/3100/27002-13, NIST 800, SCADA, OT Architectures. ● Developed centralized risk management processes and governance. ● Cloud assessments and migrations to include Microsoft Azure, Amazon web services. ● Application security recently reviewed developed within the last year include: ✓ Database monitoring tool SecureSphere. ✓ Data encryption tool HPE Voltage. ✓ VPN and MDM tool Netmotion. ✓ VPN MDM solution AirWatch ✓ Call recording software for PCI compliance Verint.
Sr. Systems Engineer
Walmart
Bentonville, Arkansas
● Create, plan, schedule and manage various and diverse risk-based cybersecurity risk assessments for diverse projects spanning various areas such as cloud, HIPAA, PCI, SOX for domestic and international business units and engaging with C-Suite executives. ● Perform application security reviews of critical assets with higher level exposure utilizing SANs top 20, OWASP top ten, as well as prescribing and reviewing results of several types of penetration tests and fortify scans etc. ● Broad business approach by serving as a bridge, provisioning information flow between the differing business units of the enterprise, an advocate of security awareness training. ● Liaise cross functionally with Infrastructure, and other operating teams to assess and identify technical, compliance and legal risks within each domain. ● Instrumental in the development of a risk centric annual audit plan utilizing the audit risk model consisting of over 225 auditable entities. ● Conduct business, third party and supplier vendor calls to determine the vendor’s level of risk by conducting questionnaire and onsite reviews of vendor’s information security program utilizing a number of different frameworks such as ISO 270002-15, COBIT, knowledge of regulatory requirements and industry standards such as HIPAA, HITRUST, SOX, PCI, GLBA, NIST. ● Advanced knowledge of Information Security and Auditing trends, competitive edge activities and advanced products, processes, and service such as the eGRC tool (RSA Archer), Service Now. ● Provide consultations for new network architectural designs to identify and contain emerging threat trends. ● Track status of vulnerabilities through accurate metrics reporting. ● Prep the organization for the annual PCI assessments as well as drove remediation for identified vulnerabilities.
Consultant- Cybersecurity Architect
HSBC
Mettawa, Illinois
∙ Subject matter expert for software programming and application security including threat modeling. Introduced an application security audit program for assessing software security for critical online banking and transaction processing applications. ∙ Developed and utilized IT audit work programs and tools to review, assess and test information system controls and security at the various HSBC business units. Specific audit areas include Information Security & Privacy, Networks Security, IT Governance, Database Administration, Computer Operations, Systems & Development, Business Continuity / Disaster Recovery Planning, and Client Services. ∙ Developed and introduced actionable and achievable strategic initiatives for Corporate Audit surrounding external focus, business acumen, strategic agility and collaboration. ∙ Trained and prepared leaders ahead of regulatory (FFIEC) examinations and visits. Provided advisory services to business units in support for regulatory and client inquiries relating to audit, risk and compliance. ∙ Used ingenuity to enhance the audit reports by including metrics and graphical representation to innovatively reflect issues and risks to executive management and the audit committee. ∙ Developed and presented quarterly audit analysis reports for executive management focusing on emerging risks and trends supported by matrices for IT, Finance SOX, and SAS70 audits as well as regulatory examinations. ∙ Lead special investigations and other Corporate Audit initiatives and special projects including internal fraud investigations. ∙ Demonstrated an advanced knowledge of information security and auditing trends, Competitive edge activities and advanced products, processes and services. ∙ Demonstrated strength in problem solving, conflict management, staff development, team building, organizational leadership and relationship management.
Consultant
Walgreens
Information Security Architect Third Party Vendor Assessment and Security Risk Audit Risk Analysis and Risk Management
Sr Network Engineer
City Colleges of Chicago
∙ Enterprise network support to all 15 remote locations and the College HQ ∙ Architecture, design and support to Checkpoint firewall and Cisco Pix systems, Juniper and Blue Coat firewalls. ∙ Load balancing enterprise application web servers via Netscaler appliances. ∙ Installation and configuration of Netscaler applications, configuration of virtual servers, SSL offload, rate-limiting, Security certification via Verisign. ∙ Network monitoring via WhatsupGold, Kiwi, NetCrunch, HEAT, VMware. ∙ Planning: establish policies that minimize the potential for infection. ∙ Detection: Correlate events across multiple platforms for accurate threat analysis ∙ Mitigation: network and endpoints simultaneously eradicating viruses/worms. ∙ Prevention: Keep noncompliant or infected endpoints from connecting to the network. ∙ Hardware: CHECKPOINT R55, R60 running on UNIX secure platform and HP hardware, also have experience running checkpoint on Nokia appliances, Checkpoint NG FP3. ∙ CISCO: Configuration, design, deployment, of hardware platforms 7200, 7507, 7606, 6506, 6509, 4912, 3550, 3548, 2950. WIRELESS CHANTRY, NETSCALER, DS3, OS3, GIGAMAN. RST, 802.1Q ∙ Software: includes NESSUS, NMAP, BMC PATROL, TIVOLI DESKTOP, WINSCP, KIWI CATTOOLS, NETCRUNCH, WHATSUPGOLD, PUTTY, CISCO NETWORK ASSISTANT, 3COM NETWORK SUPERVISOR, WEBSPHERE,WEBLOGIC,JBOSS,PROTOCOLS: OSPF, RIP, TCP/IP, SPX/IPX, RIP,EIGRP,IGRP, ACLs, VACLs, IGP,MPLS, EGP,VLAN, SPANNINGTREE PROTOCOL, VTP, DOT1Q, ISL, DTP, HDLC, PPP, H320, H323, IEEE, IRB,DHCP,DNS,WINS,NTP, FRAMERELAY, LMI, QoS, PAGP,LACP, LDAP, VMware. ∙ Strong knowledge of QoS (quality of service) and DoS, as well as predictive modeling stress testing, and adherence to IEEE standards. ∙ VLAN configuration, network segmentation as well as bandwidth management. ∙ Considerable understanding of WAN base service including broadband, VPN service and Architecture, firewall service, Web Hosting/application service and Ecommerce.
Education
Kharkiv State Technical University of Construction and Architecture
Electrical and Electronics Engineering
Bachelor's and Master degree in Electrical Engineering
Edward Awonaike's Contact Information
Phone
Find the Right Leads
Find Verified Contact Data

What LeadContact does well
Find verified emails, phone numbers, and decision-makers with 98% accuracy.

Find Leads
Find the right people by company, role, industry, location, and more.
925M+ professional profiles

Find Emails
Access verified email addresses for your target contacts.
657M+ emails

Find Phone Numbers
Get cross-validated phone data from multiple top sources.
239M+ phone numbers
More Accurate. Lower Cost.
Find contact data in 1 tool with 98% accuracy
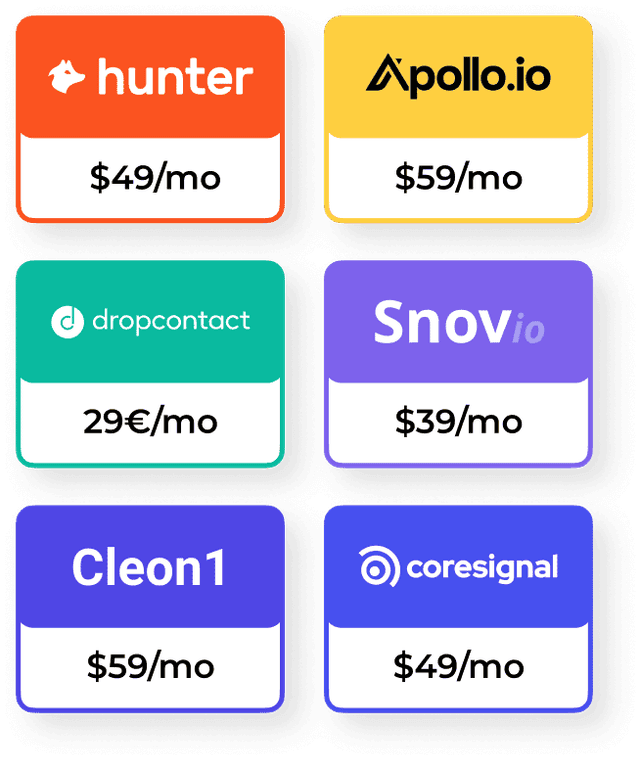
LeadContact integrates leading enrichment tools to deliver more accurate contact data—without paying for each one.

Great conversations start with the right contact.
It’s time to find yours.