
Ikenna Cyril Nwafor CCISO, CISSP, CISM, CISA, GICSP, GSLC
Principal Consultant - Cybersecurity
About
As a seasoned and solution-focused cybersecurity leader, I bring deep expertise in Governance, Risk, and Compliance (GRC) across both public and private sectors. I specialize in driving end-to-end security programs that safeguard digital assets, infrastructure, and operational environments. From developing enterprise-wide GRC frameworks to overseeing security standards, policies, and procedures, my approach is anchored in aligning cybersecurity initiatives with business strategy and regulatory requirements. With extensive experience delivering tactical and strategic recommendations on cyber threats, disaster recovery, and IT/OT security controls, I’ve successfully led critical functions such as risk assessments, internal audits, and compliance with ISO, PCI DSS, NIST CSF, and other frameworks. I have a track record of elevating security maturity levels, enhancing organizational resilience, and reducing exposure through measurable, data-driven initiatives. My collaborative leadership style has empowered teams, streamlined vendor relationships, and improved threat detection and response across board. I’m passionate about fostering a culture of security awareness and continuous improvement. I’ve led confidential investigations, mentored teams, and developed impactful training and policy programs to reinforce secure business practices. Whether partnering with executive leadership or operational teams, I strive to create actionable strategies that protect critical assets while enabling innovation and efficiency.
Canada
Calgary
Computer & Network Security
Information Technology and Operational Technology Management, Cross-functional Team Leadership, Communication, Program Management, Cybersecurity Advisory, Third-Party Vendor Management, Cross-functional Collaborations, Project Management, Cross-team Collaboration, Strategic Leadership, Time Management and Adaptability, Cybersecurity Program Management, Governance, Risk Management, and Compliance (GRC), Cybersecurity Maturity Assessments, Cybersecurity Awareness and Education, Cloud Security, Network Security, Security, Cisco, ITIL
Experience
Principal Consultant - Cybersecurity
Icon Cyber Services
Calgary, Alberta, Canada
As Principal Consultant - Cybersecurity of Icon Cyber Services, my focus is on helping organizations strengthen their security posture, achieve compliance, and build digital trust. I provide executive-level advisory and hands-on program delivery across multiple industries, aligning cybersecurity governance with business strategy and regulatory requirements. Key Focus Areas: • Governance, Risk & Compliance (GRC): Design and implement cybersecurity and regulatory frameworks (NIST, ISO 27001, SOC 2, CIS CSC); lead audit readiness, maturity assessments, and remediation programs. • Cybersecurity Strategy & Program Management: Deliver enterprise-wide security programs and roadmaps, providing Virtual CISO (vCISO) advisory and executive guidance to boards and leadership teams. • Security Operations & Incident Response: Support SOC optimization, SIEM/EDR implementation, and coordinated threat detection and response capabilities. • Compliance & Assurance: Drive NIST CSF and ISO 27001 assessments/alignment, vendor and third-party risk assessments, CMMI Maturity, and regulatory compliance initiatives (PCI DSS, NERC CIP). • Cloud & Infrastructure Security: Develop secure cloud architectures (Azure, AWS, GCP), strengthen IAM/RBAC controls, and integrate DevSecOps security best practices into enterprise operations. • Awareness & Resilience: Lead cybersecurity training, phishing simulations, and business continuity/disaster recovery (BCDR) initiatives to foster security-first cultures.
Senior Project Manager, Cybersecurity
City of Calgary

Calgary, Alberta, Canada
In this role, I am responsible for overseeing and coordinating multiple cybersecurity projects simultaneously, ensuring they are completed within defined timelines and budget parameters. I provide strategic direction and leadership to project teams, work closely with external vendors, and engage with senior stakeholders to align initiatives with organizational goals. I guide the successful delivery of cybersecurity programs using a mix of sequential and agile methodologies, developing clear project documentation such as charters, work breakdown structures, and timelines to keep efforts organized and on track. A key part of my role involves fostering strong collaboration between business and technical teams, helping to establish open communication channels that promote a shared understanding of objectives, risks, and progress. By maintaining focus on strategic alignment, I support leadership decision-making through wellinformed consultation on project scope, timelines, and resourcing. I also manage stakeholder relationships with transparency and consistency, which has contributed to greater trust, clearer expectations, and more successful outcomes across the organization’s cybersecurity initiatives.
Manager, IT Security
Peavey Industries LP
Alberta, Canada
As Manager of IT Security at Peavey Industries LP, I was responsible for safeguarding business operations across more than 90 retail locations through the design and implementation of a comprehensive enterprise-wide cybersecurity program. I developed and executed a formal cybersecurity risk management framework and conducted proactive security assessments to strengthen the organization's overall risk posture. By working closely with executive leadership, I ensured that cybersecurity strategies were fully integrated with the company’s broader IT and business objectives, including optimal budget allocation and roadmap development. I led the deployment and management of advanced cybersecurity solutions—such as Forti-EDR, FortiClient, FortiSIEM, and File Integrity Monitoring (FIM)—to enhance real-time threat detection and response capabilities. I also supported secure digital transformation by advising stakeholders on security requirements for both on-premises and cloud-based systems, while managing outsourced Security-as-a-Service (SECaaS) partners to ensure swift and effective incident handling. Through this role, I significantly improved Peavey’s cybersecurity maturity rating within a year—by driving third-party assessments and implementing remediation plans aligned with industry frameworks like NIST CSF, CIS Controls v8, and PCI DSS. I led the company to PCI compliance in 2022 by closing identified gaps and deploying effective security controls. Notably, I reduced phishing vulnerability by nearly 50% through a strategic cybersecurity awareness program and developed a Cybersecurity Ambassador initiative to help embed a culture of cyber awareness across the organization. I also improved vendor management, negotiated high-impact contracts, and aligned budget planning to boost operational efficiency and return on investment.
Lead, Security Architect and Standards
Alberta Health Services
Calgary, Alberta, Canada
At Alberta Health Services, I played a key role in elevating the organization’s cybersecurity capabilities by maintaining and evolving the strategic documentation that guided the Information Security Management (ISM) team. My work ensured alignment with internal business standards and industry best practices, particularly through comprehensive security architecture reviews and ongoing consulting support provided to enterprise architects. I actively collaborated with stakeholders across departments to develop, refine, and enforce security standards, helping to ensure the consistent application of cybersecurity best practices throughout the organization. My efforts were instrumental in promoting secure-by-design principles across various initiatives. In support of cloud adoption efforts, I provided detailed security guidance for both Azure and AWS environments—developing risk assessment templates, setting technical standards, and advising on secure implementation approaches. I also contributed to stronger security postures across numerous enterprise projects by offering tailored architectural input and risk-based recommendations, enabling project teams to proactively identify and mitigate potential vulnerabilities early in the development lifecycle.
Program Director
ISACA Calgary
Calgary, Canada Area
Lead, Cyber Security
TransAlta
Calgary, Canada Area
During my tenure at TransAlta, I played a pivotal role in enhancing the company’s cybersecurity posture through the strategic oversight of five critical cybersecurity service areas: Security Operations Center (SOC), Identity and Access Management (IAM), Governance, Risk & Compliance (GRC), security awareness, and End User Computing (EUC). I designed and led a comprehensive cybersecurity awareness and training program that significantly reduced the organization’s phishing susceptibility rate, fostering a culture of security awareness across the business. I was responsible for aligning the enterprise’s cybersecurity framework with ISO 27001 standards by developing an IT security program backed by clear policies, procedures, and performance indicators. I further advanced incident detection and response capabilities by strengthening SIEM operations and integrating external threat intelligence to proactively address evolving threats. This also involved improving SOC effectiveness and driving vendor accountability through well structured RFP processes and third-party management. My role also included budgeting responsibilities, where I ensured optimal allocation of resources to support key cybersecurity initiatives. I implemented a formal security risk assessment process, fully integrated with the PMO, to improve governance and risk visibility. Additionally, I managed CIS, NIST CSF, and ISO 27001 assessments and guided efforts that led to NERC-CIP compliance for 35 OT facilities across North America. As a leader, contributed to the growth of the cybersecurity team, and actively contributed to shaping TransAlta’s three-year IT and cybersecurity strategy and roadmap.
Senior Analyst, Cyber Security Governance & Risk Management
TransAlta
Calgary, Alberta, Canada
Senior Information Security Specialist
TransAlta
Calgary, Canada Area
Senior Information Security Specialist
Wipro
Edmonton, Canada Area
Enterprise Risk Services Consultant
Deloitte
Edmonton, Canada Area
Data Loss Prevention (DLP) Strategy & Risk Assessment I helped strengthen an organization’s ability to prevent sensitive data from being leaked or misused. This involved reviewing how well their existing processes, security tools, and governance structures were protecting information. After identifying weaknesses, I provided clear and practical recommendations for how to improve. I also analyzed how data could be exposed during transmission, storage, or active use, helping the organization better understand its risk exposure. To make the strategy effective, I worked closely with internal teams to pinpoint which types of data were most sensitive and needed the highest level of protection. This ensured that our DLP efforts were in line with the business’s goals and compliance needs. IT Security Controls Testing (Audit Function) In my role as a Security Analyst, I reviewed a wide range of IT practices—like how access is given to users, how changes to systems are tracked, how backup and recovery plans are managed, and how security incidents are handled. Vulnerability Assessment & Technical Security Review As part of a security improvement project, I examined the internal network and firewall setups to find any weaknesses that could be exploited. I used industry-standard tools like Nessus, Nmap, and Nexpose to scan for vulnerabilities in the infrastructure. PCI DSS 2.0 Readiness Assessment For a company preparing for PCI DSS compliance (which is required when handling credit card data), I helped identify all systems that processed or stored payment information. I worked with multiple teams across the business to ensure we had a complete picture. I then conducted a gap assessment to evaluate how existing security controls measured up to PCI DSS 2.0 standards. Based on the findings, I created a roadmap that outlined exactly what steps needed to be taken to meet compliance requirements and protect customer data.
Management Information Systems Graduate Research Assistant
Concordia University of Edmonton
Edmonton, Canada Area
IT Support Analyst - (UK, China, Hong Kong, Belgium, South Africa, Dubai, & Italy)
Static Control Components (Europe) Ltd
Education
Concordia University of Edmonton
Information Systems Security Management
Related Coursework - Business Continuity & Disaster Recovery Planning, Cryptography and Secure Network Communications, Information Security & Risk Management, Security Policies & Procedures, Digital Forensics, System Development & Project Management, Penetration Testing & Vulnerability Assessment, Operations Security, Financial Management
SANS Technology Institute
MGT 512: Security Leadership Essentials For Managers
SANS Technology Institute
SANS Technology Institute
University of West London
Electronics with Communications Engineering
Related Coursework - Engineering Software Development, Signal Systems Analysis, Communication Networks, Communication Systems, Digital Signal Processing
Ikenna Cyril Nwafor CCISO, CISSP, CISM, CISA, GICSP, GSLC's Contact Information
Phone
Find the Right Leads
Find Verified Contact Data

What LeadContact does well
Find verified emails, phone numbers, and decision-makers with 98% accuracy.

Find Leads
Find the right people by company, role, industry, location, and more.
925M+ professional profiles

Find Emails
Access verified email addresses for your target contacts.
657M+ emails

Find Phone Numbers
Get cross-validated phone data from multiple top sources.
239M+ phone numbers
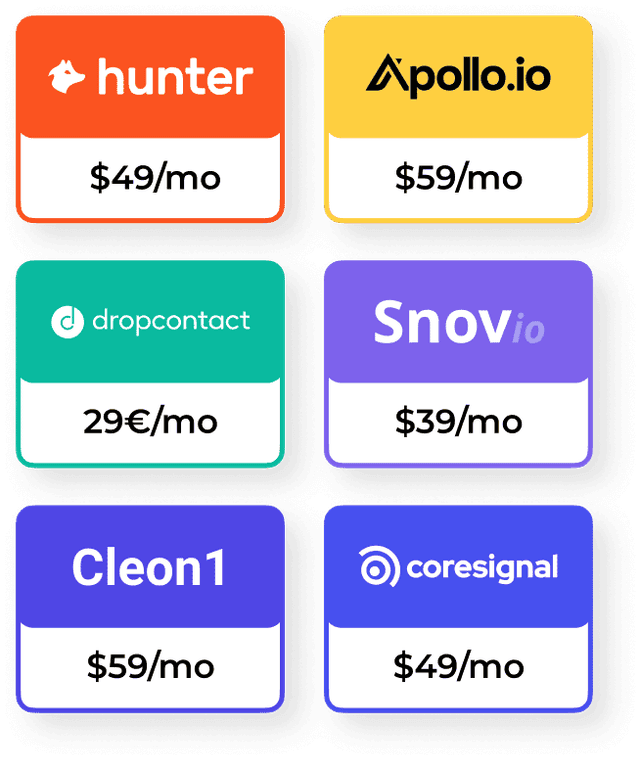
More Accurate. Lower Cost.
Find contact data in 1 tool with 98% accuracy
LeadContact integrates leading enrichment tools to deliver more accurate contact data—without paying for each one.

Great conversations start with the right contact.
It’s time to find yours.