Fahad Khan CISSP-CISM-CCIE
CISO (Chief Information Security Officer) Country Head @ Apollo Hospitals
About
🌐 Summary: With over 19 years of experience in information security, I currently serve as the Chief Information Security Officer (CISO) at Apollo Hospitals, overseeing the safeguarding of the organization’s security policies and developing and implementing cybersecurity strategies that protect global enterprises across the automobile, manufacturing, Healthcare, and retail sectors. As the Global Head of Cybersecurity, I focus on safeguarding digital assets, ensuring business continuity, and driving security frameworks that align with industry standards. 🌟 Core Competencies: I specialize in a wide range of cybersecurity areas, including developing robust security strategies, managing enterprise cybersecurity architecture, and ensuring IT governance, risk management, and compliance. My expertise extends to securing Operational Technology (OT) environments, implementing endpoint, network, and mobile security, and managing identity and privileged access. I have hands-on experience in running Security Operations Centers (SOC), incident response, and business continuity planning. Additionally, I excel in third-party risk management, threat and vulnerability assessments, and fostering a cybersecurity-aware culture through training. My leadership skills include building high-performing teams, managing projects, and optimizing cybersecurity budgets to align with business objectives. 🛠 Skills & Certifications: Technical Skills: Checkpoint, Palo Alto, FortiGate, McAfee SIEM, Symantec Anti-Spam, Tenable SC, CyberArk PAM, Zimperium Mobile Threat Prevention, Office 365, Azure AD, CASB, and more.Certifications: CISSP (Certified Information System Security Professional), CISM (Certified Information Security Manager), CCIE (SECURITY CERTIFIED SECURITY EXPERT (CISCO),RHCSS (Red Hat Certified Security Specialist) 💡 My Approach: I adopt a proactive and holistic approach to cybersecurity, viewing it as a strategic business enabler. By embedding security into every layer of the organization, I drive resilience, operational efficiency, and innovation. My goal is to protect digital assets' integrity, confidentiality, and availability while supporting the organization's growth amidst an ever-changing threat landscape. 🤝 Why Connect with Me? I am passionate about exploring innovative cybersecurity solutions and working with professionals who share a vision for a safer digital world. Let’s connect to discuss strategies, exchange knowledge, or explore new opportunities to secure our digital future!
India
Bengaluru
Information Technology & Services
Security Research, Data Security, Security Compliance, Security Certification, PCIDSS, U.S. Health Insurance Portability and Accountability Act (HIPAA), generic AI, Automation, Info Sec, Agentic AI Development, Security Architecture Design, Certified Information Security Manager (CISM), IT Security Operations, Security Policy Development, Information Security Governance, OT Security, AI Cyber , AI security Cloud , CISO, Application Security Architecture
Experience
CISO (Chief Information Security Officer) Country Head
Apollo Hospitals

Bengaluru
As CISO safeguarding the company’s Security policy and maintaining reputation for security excellence. AI SOC IMPLEMENTATION, SIEM SOLUTION IMPLEMENTATION- WITH 200+ team members across india. TOP 4 ON Going Projects AI Cyber security & cloud security projects: -As CISO focus on securing the organization’s assets,while enabling business growth. A proactive leader who anticipates risks and implements effective solution SIEM(SPLUNK, MICROSOFT Sentinal) .impactful security measures , AI Security policy ISMS policy making. • Maintains the highest standards of integrity and communication, earning the trust of internal and external stakeholders. • Brings a high level of energy and a sense of urgency to AI security initiatives, fostering a culture of awareness and resilienceacross the organization. This involves not only leading by example but also implementing comprehensive training programs and communication strategies to ensure that all employees understand the importance of cybersecurity.• Demonstrates exceptional ability to thrive in a team-oriented environment, collaborating effectively with cross-functional. • Rapidly evolving AI security landscape. This involves proactively identifying and mitigating emerging threats to protect the organization’s data and IT infrastructure. Additionally, maintaining strict adherence to all relevant • regulatory frameworks, ensuring not only meets but exceeds compliance standards.
Vice President (Cyber Security & Cloud Security Strategy Execution & implementation, Retailing
EY-Parthenon
Bengaluru
: Cyber security & cloud security projects:- LEAD TSE(Transition Strategy & Execution) cyber security, Planning, Architecture & Post Merge Integartion, Retalil, LEAD information security Transaction, Design Advisory Security solutions with DD (Due Diligence) & Delivery. Total 6 Security Project Accomplish: 1)PROJECT: Marriot Internationa(USA): -Reccomended design & developed security Patterns for Access control , Intigrity services Architectures & landscape 2)APPLICATION MIGRATION:-merging 3 companies (raventex,apexon,vaste) into one OMEGA HEALTH USA. With AWS CLOUD MIGRATION AWS ,Data Security & Compliance. Managed & complete information security project for IAM PROJECT (NASM NATIONAL AVIATION SYSTEM MANAGEMENT ) at national informatic center. With IAM tools like SAIL POINT , WEB EAGLE, RSA, IBM. 3) Cagile project - Vendor management policy 3rd party information security due diligence IT asset disposal policy For secure disposal of equipment and information Business continuity policy Crisis management and incident response processes Disaster recovery policy Acceptable methods for disaster recovery planning, preparedness, management and mitigation of IT systems and services Clean Desk policy Part of ISO 27001/17799 compliancy and basic standard Wireless access policy Wireless technology baseline set of requirements Risk management policy Information and guidance on risk management Patch management policy Regular security updates and patches
Senior Principal Architect
Deloitte
Hyderabad
1)PROJECT: Managed & complete information security project for IAM PROJECT (NASM NATIONAL AVIATION SYSTEM MANAGEMENT ) at national informatic center. With IAM tools like SAIL POINT , WEB EAGLE, RSA, IBM. 2)NICNET (NATIONAL INFORMATICS CENTER NETWORK SECURITY) 3)SPUI (STATE PROJECT IMPLEMENTATION UNIT) 4)NICSI(NATIONAL INFORMATICS SECURITY SERVICE) 5)IMPLEMENTATION OF NAMS(NATIONAL AVIATION MANAGEMENT SECURITY PROJECT at NATIONAL INFORMATICS CENTER. With 5P(Security Principles) Adoption , NIC continued high rated growth prospects. Experiences in Implementation Handling & Leading Next Gen SOC Team & Security incident management. ? Experience in SOC(Security Operation Center) to facilitate strong planning as per security protocol needed. ? Established NIC'S Security Standard for Protecting Government?s Critical Information Infrastructure& Improving State Cyber security through complete New Standard and Guidance with (such as ISO27001 & NIST Framework). ? Fully Expertise in SIEM Tools-(SIEM LogRhythm ver-8,, Splunk ver-6, IBM QRadar-ver7.2, ArcSight, RSA Netwitness ). ? Well-Experienced In (NIDS) Network Intrusion Detection System and Host Based (IPS/IDS)intrusion prevention system & IDS(Intrusion Detection System). ? Deployed successfully Vulnerability Assesment and penetration Testing (VAPT) in a system with Tools (wireShark,N mapper,metasploit,Nessus,John Ripper) ? Well implemented the DATA LOSS PREVENTION(Symantec endpoint DLP & Forcepoint DLP) including cryptography & PATCH MANAGEMENT TOOLS i.e solar wind patch manager. ? Grip-on IT AUDITS,RISK MANAGEMENT, IT RISK ASSESSMENT & RISK Rating for NKN (National Knowledge Network) ? Depth knowledge of various cloud services including IaaS, PaaS & SaaS with cloud security (AWS & IBM cloud). ? Fully Experienced in and Framework NIST(National Institute of Standard Technology) & PCI-DSS ,,ISO27001,COBIT&TOGAF. ? Experience in & web application Firewall(AWS-WAFs). CISCO Firewalls
Information Security Analyst
Wipro
Bangalore Urban
IT security, SELinux, firewall vulnerability Project Accomplish : 1)(NKN (National Knowledge Network): All government Edition & Educational sites of states- Design & Implement the Apllication Tools like End point protection, Encryption, Public key Infrastructure, Cryptography, patching, Intrusion detection/ Intrusion prevention system. PENETRATION TESTING web Applications, Cyber Security Standard Framework. 2)NAMS(National Aviation Management Security) SECURITY Project. Application intigrated with cyber Forensic Investigation(Network, File system , mobile Forensic) SIEM TOOLS ( LogRhyhm tools , Splunk, IBM Qradar), WAF(Web Application Firewalls) Blue coat proxy, Symantic proxy, Patch Management, wire shark ,Nessus,Aircrack Design & Implementation of Network and System Security for NATIONAL INFORMATIC CENTER(NIC). ? Manage & Handle the complete information security project for SIO (STATE INFORMATION OFFICIAL) ? Establishing disaster recovery procedure and conducting breach of Security drills. ? Developed the set of standards for design of security elements in system Application. Responsible For Information Security in a Network envoirment System. ? Measure of SECURITY AUDIT & RISK MANAGEMENT should be taken completely with all updated Tools ? Security Capabilities to provide technical support and analysis of current and proposed system / Architectures. ? Evaluates new Security Products and Security Audits. Responsible for Configuration controls of security systems and as required & design Security of current information system. ? Co-ordinate and responded to Security management center (SMC) as per regular interwall of time from Head Office. ? Prepared and delivered high- level Security briefing for various user Groups and Upper Managements.
Information Technology Security Engineer
3i Infotech Ltd.
Raipur, Chhattisgarh, India
vulnerabilities & threats, advisories, and incidents,Handle configuration and change management of SIEM solution with RSA Netwitness platform ver.11.2 * Perform IT General Control Assessment & Information security Risk Assessment. *Developing policies, procedure, standards and guidelines as per security practices. * Able to translate information security requirement into business needs and vice versa. *Executing the projects to explain the VAPT findings to technical and non-technical teams. * Track and coordinating with different teams to close the risk identified during VAPT exercise. * Solid understanding of Information Security Standards and compliance like ISO 27001, PCI DSS, OWASP, NIST. *Undertaking structured analysis of vendor proposals for the supply of new InfoSec solutions in close collaboration with the concerned business unit. * Preparing the plan for the complete project lifecycle of assigned projects and for the update of these plans during that lifecycle. *Accountable for the identification and management of project risks for each assigned project.
Security Engineer
RM Infotech
Raipur, Chhattisgarh, India
*Establishing, Implementing Security best practices within the database envoirment. *Configured and distributed Co-orporate level ? directed software security upgrade using automated networks Utilities. *Perform password complexity checks o ensure compliance with security standards, and Implemented an in house built host data Collection tool to identify anmolous activity. *Perform cyber- threat hunting process of proactively identify internal risk that might exist in IT infrastructure. *Monitor outside intelligence source to identify emerging threats and associated protection and determines how they apply to the enterprise enviorment.
Education
Central Board of Secondary Education
Central Board of Secondary Education
Fahad Khan CISSP-CISM-CCIE's Contact Information
Phone
Find the Right Leads
Find Verified Contact Data

What LeadContact does well
Find verified emails, phone numbers, and decision-makers with 98% accuracy.

Find Leads
Find the right people by company, role, industry, location, and more.
925M+ professional profiles

Find Emails
Access verified email addresses for your target contacts.
657M+ emails

Find Phone Numbers
Get cross-validated phone data from multiple top sources.
239M+ phone numbers
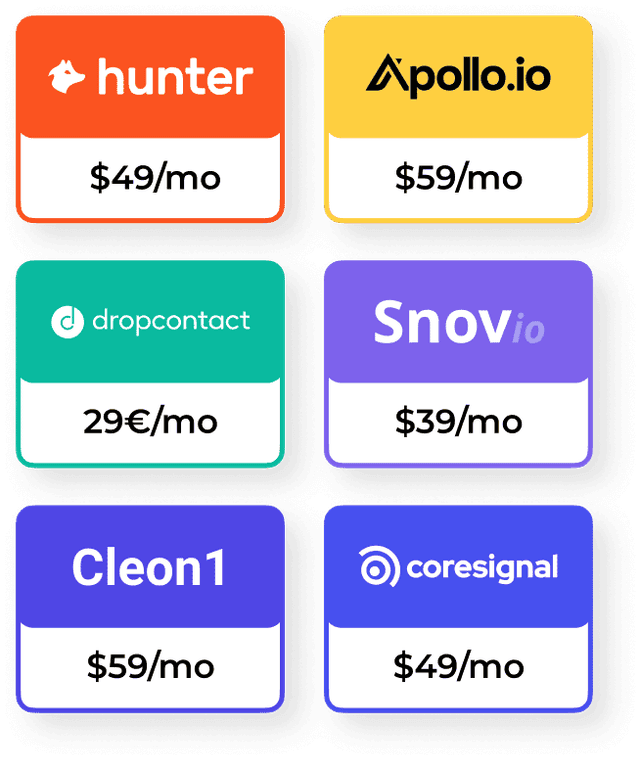
More Accurate. Lower Cost.
Find contact data in 1 tool with 98% accuracy
LeadContact integrates leading enrichment tools to deliver more accurate contact data—without paying for each one.

Great conversations start with the right contact.
It’s time to find yours.